Here is a slimmed down version of the presentation I delivered in Italy last March.
This version does not contain the part that talks about the problem (i.e. the attacks and why you need to do Application Security)
The key idea that I defend is that we can use Application Security to define and measure Software Quality
Let me know what you think
Showing posts with label Quality. Show all posts
Showing posts with label Quality. Show all posts
Friday, 6 May 2016
Sunday, 24 April 2016
Started working on new book "Measuring Software Quality using Application Security"
 Over the 3 weeks I spent in the US (in an RV with family) I started working on a book based on the ideas shown at the "New Era of Software with modern Application Security" presentation (v1.0).
The current title is "Measuring Software Quality using Application Security" and it is going to be published at LeanPub: https://leanpub.com/Software_Quality
All content is hosted on the public GitHub repo
https://github.com/DinisCruz/Book_Software_Quality/tree/master/content, where you can also see a number of issues I plan to address (including areas for research)
I am currently in the brain dump stage of development, where I'm adding the content I want to talk about (in a kinda-structured way). The idea is to expand the bullet points into text and normalise the content in logical areas (some topics already have a first pass at expanding the ideas into final text).


Wednesday, 23 March 2016
When talking about Application Security and Software Quality, Pollution is a much better analogy than Technical Debt
One of the analogies that I make in my "New Era of Software with modern Application Security" presentation is that Pollution is a much better way to describe quality (and security) issues (vs Technical Debt):


This analogy is inspired by David Rice's amazing keynote at OWASP AppSec USA 2010 "Upon the threshold of opportunity" (which you can see the video here)
David Rice is the author of the also amazing Geekonomics book, which really shows The Real Cost of Insecure Software
Unfortunately, David Rice after going to work for Apple, seems to have disappeared from the internet, which is a great loss for the world, since he was doing amazing research (of course that I'm sure he is doing great stuff for Apple, but it is a shame that we are not able to learn from him anymore)
David's http://blog.geekonomicsbook.com/ book site is down, but luckily the wayback machine was able to get a copy of the page with the abstract of this talk:
Related posts:


This analogy is inspired by David Rice's amazing keynote at OWASP AppSec USA 2010 "Upon the threshold of opportunity" (which you can see the video here)
David Rice is the author of the also amazing Geekonomics book, which really shows The Real Cost of Insecure Software
Unfortunately, David Rice after going to work for Apple, seems to have disappeared from the internet, which is a great loss for the world, since he was doing amazing research (of course that I'm sure he is doing great stuff for Apple, but it is a shame that we are not able to learn from him anymore)
David's http://blog.geekonomicsbook.com/ book site is down, but luckily the wayback machine was able to get a copy of the page with the abstract of this talk:
-
In the 1960s, pollution in the United States reached a breaking point. Large corporations, by and large, had been unresponsive to environmental issues leaving the nation's skies filled with smog, rivers filled with sludge, forests defoliated by acid rain, and fresh water lakes declared "dead." The natural heritage of the nation was being destroyed by its industrial prosperity.
The U.S. response was a series of less-than-satisfactory regulatory attempts to correct for substantial environmental damage. Faced with serious and costly legacy issues of industrialism however, many companies stonewalled and delayed for much of the 1980s and 1990s, emphasizing legal compliance and reactionary practices over real progress. The turn of the century ushered in a fresh perspective in corporate America, with companies like GE, DuPont, and Wal-Mart actively pursuing sustainability initiatives linked to corporate performance, transforming environmental crisis into financial opportunity. What happened?
Within the story of the U.S. battle against environmental pollution lies key lessons for confronting the equivalent of pollution in cyberspace: software vulnerabilities. The toxic effluence of software vulnerabilities leave networks saturated with spam, computers clogged with malware, and servers defoliated of sensitive private data.
To date, a series of less-than-satisfactory regulatory attempts – such as PCI, SOX, and data breach laws – have been enacted to address what appears to be widespread unresponsiveness to the substantial harm to the global digital eco-system caused by unrestricted vulnerability dumping. Faced with serious and costly legacy issues of poorly implemented software systems however, many companies continue to stonewall or delay security programs, emphasizing legal compliance and reactionary practices while demonstrating no real improvement. What would it take to change this, to turn the crisis of “pollution” in cyberspace into an opportunity?
This keynote highlights a possible fresh perspective, putting software security into the context of social responsibility linked to corporate performance, illustrating how the software market - like corporate America - stands upon the threshold of its greatest opportunity.
Related posts:
Sunday, 20 March 2016
"New Era of Software with modern Application Security" presentation (v1.0)
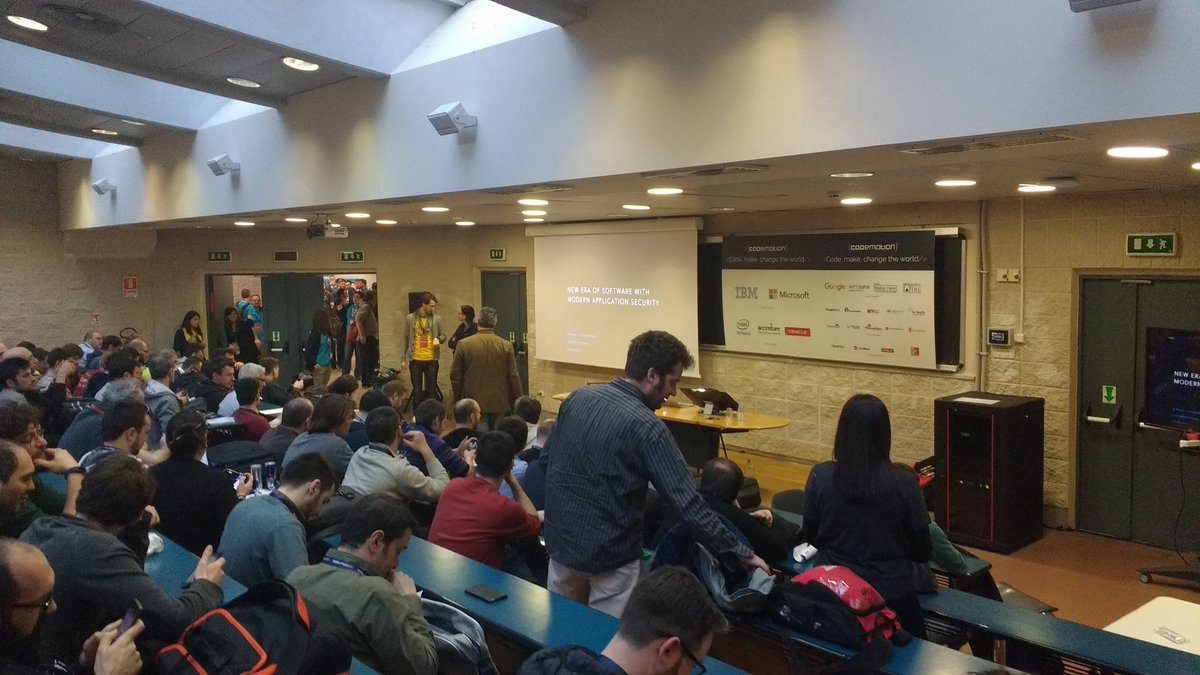 This is the final slide deck of the "New Era of Software with modern Application Security" presentation I delivered at Codemotion Rome, which was a developer-focused conference (with 2000 tickets sold).
 Description: "This presentation will start with an overview of the current state of Application Insecurity (with practical examples). This will make the attendees think twice about what is about to happen to their applications. The solution is to leverage a new generation of application security thinking such as: TDD, Docker, Test Automation, Static Analysis, cleaver Fuzzing, JIRA Risk workflows, Kanban, micro web services visualization, and ELK. These practices will not only make applications/software more secure/resilient, but it allow them to be developed in a much more efficient, cheaper and productive"
Sunday, 28 February 2016
Thinking of writing a book called "Measuring Software Quality using Application Security"
This book will be based on the ideas I've been talking about in my "New Era of Software with modern Application Security" presentation.
The plan is to use my experience with Leanpub (where I have published 7 books), with the content being hosted on GitHub and published early and ofter.
The plan is to use my experience with Leanpub (where I have published 7 books), with the content being hosted on GitHub and published early and ofter.
Saturday, 27 February 2016
Is Quality is a measure of how successful a product is in what it is SUPPOSED to do?
Here is a question I received on the concept "Application Security can be used to define and measure Quality" (slides here)
Quality is a measure of how successful a product is in what it is SUPPOSED to do.I think that measuring Quality by only looking at the success rate of a product is a very narrow definition of Quality.
AppSec is a measure of how many and what things product does that it is NOT SUPPOSED to.
These two are not related. A startup may have a good quality product full of security holes, and a bank may have a highly secure product that is also of great quality.
Friday, 26 February 2016
Video for my LSCC presentation on: New Era of Software with modern Application Security
Skillsmatter has just published the video of the presentation I delivered last week at the LSSC (London Software Craftsmanship Community)
You can see it here:
https://skillsmatter.com/skillscasts/7582-new-era-of-software-with-modern-application-security
You can see it here:
https://skillsmatter.com/skillscasts/7582-new-era-of-software-with-modern-application-security
"New Era of Software with modern Application Security" updated presentation (v.0.6)
Here is the updated version of the talk I delivered last week at the LSCC (this time around delivered at the OWASP London Chapter)
There are a number of new slides, but it is still far from complete :)
Please take a look at the slides and let me know what you think of them? (and what can be improved for the next version)
There are a number of new slides, but it is still far from complete :)
Please take a look at the slides and let me know what you think of them? (and what can be improved for the next version)
Friday, 19 February 2016
V0.5 of "New Era of Software with modern Application Security" presentation
Here is my first pass at creating the "New Era of Software with modern Application Security" presentation, which I will deliver as a Keynote at the Codemotion Rome developer conference (March 19th)
This is the version that I presented yesterday at the London Software Craftsmanship Community event and its video is here
Interestingly, one of the concepts that I arrived at (when working on the slides) was that Application Security can be used to define and measure Quality.
This is something that I have been thinking about for a long time, and I'm starting to find a way to explain how I'm able to use Application Security to help developers to create better applications (with not only better security, but with better quality)
Please take a look at the slides and let me know what you think of them? (and what can be improved for the next version)
This is the version that I presented yesterday at the London Software Craftsmanship Community event and its video is here
Interestingly, one of the concepts that I arrived at (when working on the slides) was that Application Security can be used to define and measure Quality.
This is something that I have been thinking about for a long time, and I'm starting to find a way to explain how I'm able to use Application Security to help developers to create better applications (with not only better security, but with better quality)
Please take a look at the slides and let me know what you think of them? (and what can be improved for the next version)
Subscribe to:
Posts (Atom)